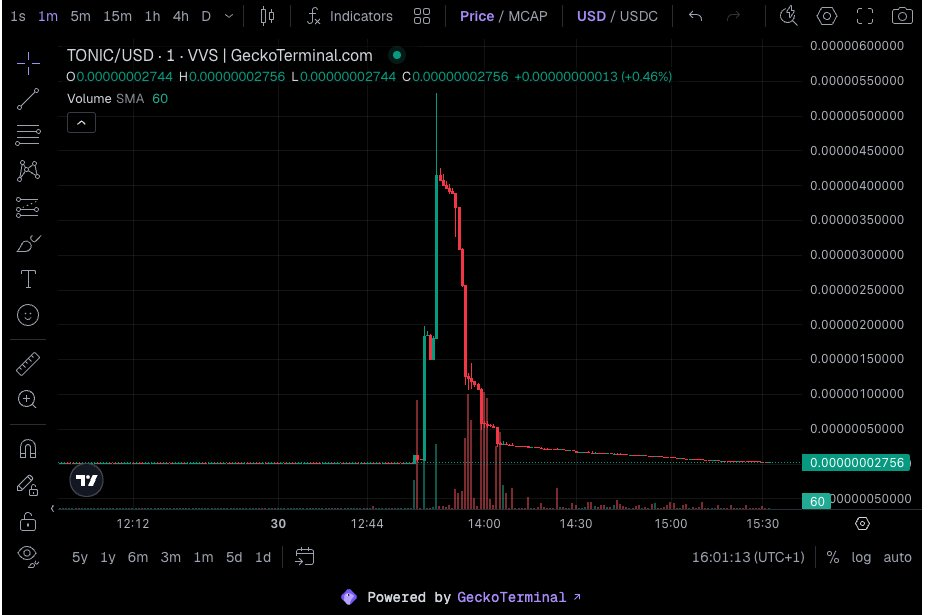
The attacker exploited the low liquidity of TONIC to manipulate its price, driving it up by approximately 100x in around 20 minutes and borrowing about $74 million from Tectonic.
Written by: ChandlerZ, Foresight News
On August 30, Tectonic, a lending protocol in the Cronos ecosystem, was attacked, and Cronos subsequently halted block production. Researcher Weilin Li initially tracked approximately $66 million, of which around $6 million was transferred to Ethereum and about $60 million remained in three addresses on Cronos; he later discovered another attacker address holding roughly $8 million. PeckShield subsequently estimated the loss at approximately $74 million.
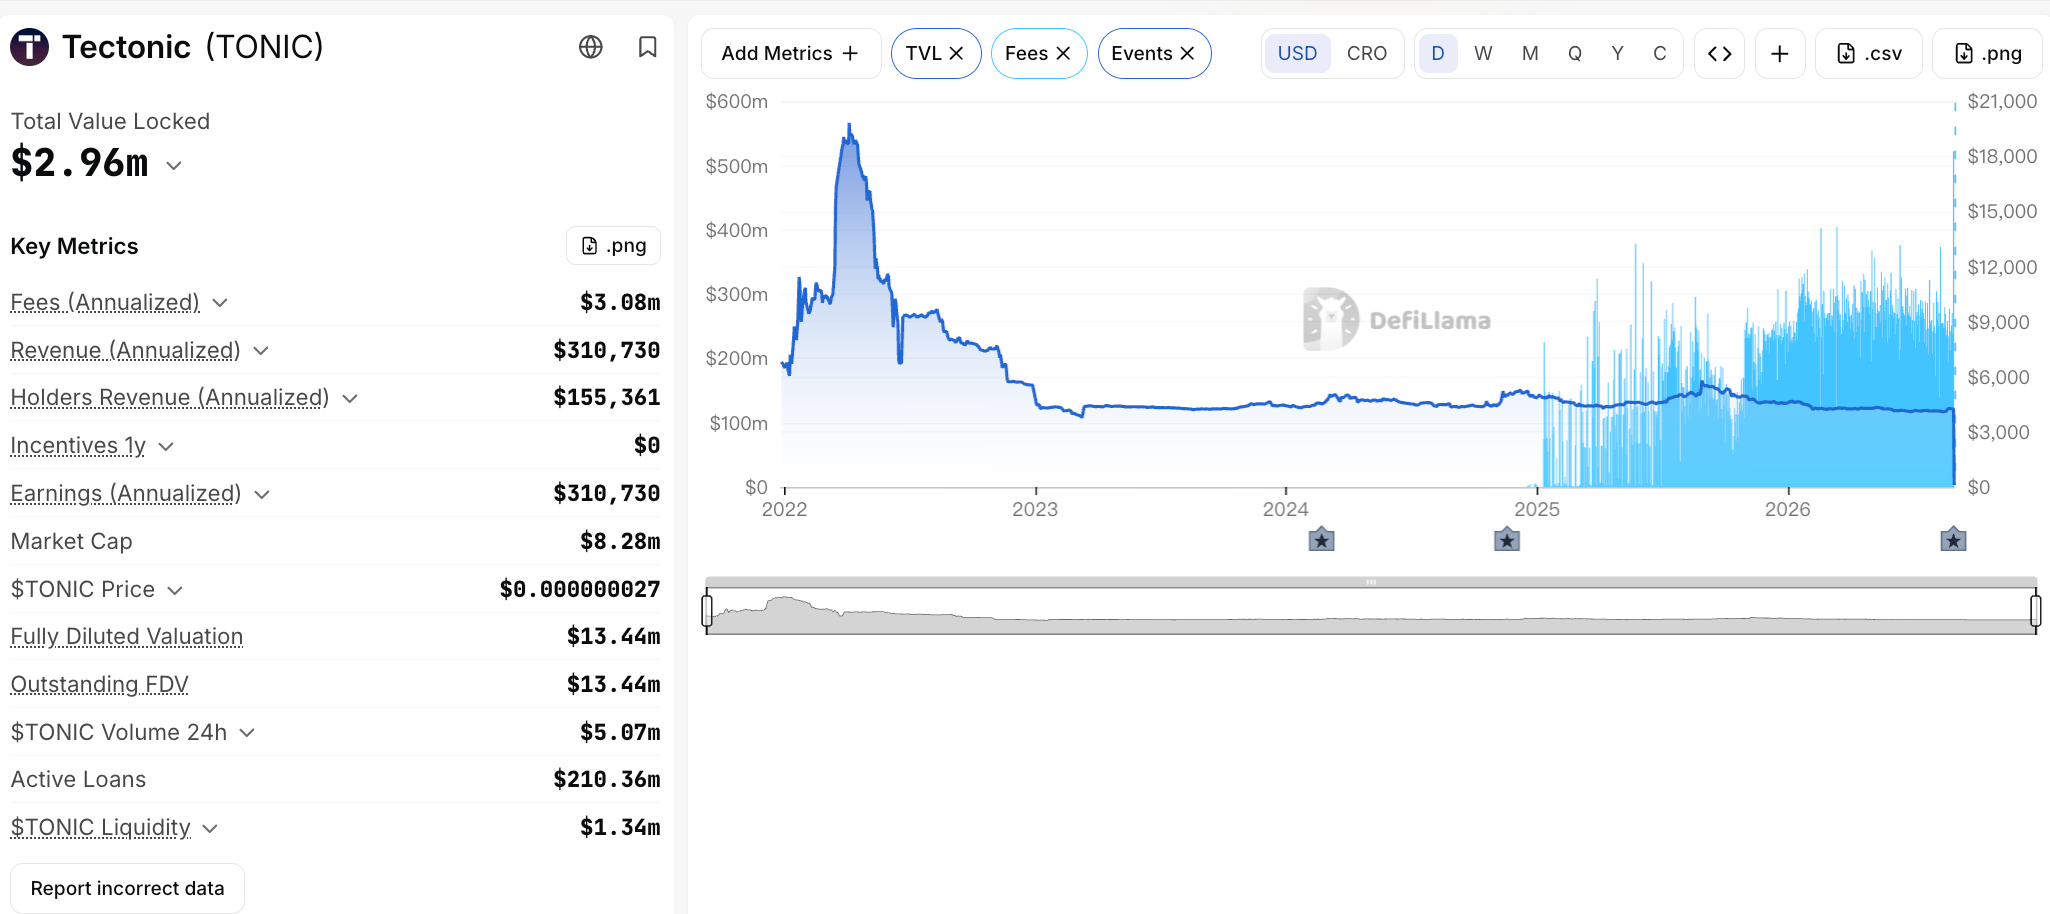
Cronos was originally developed by Crypto.com, while Tectonic is operated by an independent team. Tectonic allows users to deposit assets such as USDC, USDT, CRO, and WBTC into pools to earn interest, and borrowers can borrow liquidity from the pools after collateralizing assets. Before the incident, Tectonic was the largest lending protocol by locked value in the Cronos ecosystem. DefiLlama showed that Tectonic's total value locked (TVL) was approximately $120 million, with active loans of around $82.7 million.
As of August 31, Tectonic's TVL had dropped to below $3 million, remaining at only about 2.5% of its pre-incident value.
Tectonic's borrowed assets come from shared pools provided by depositors, who receive tToken share certificates. Loan limits and withdrawal requests are automatically executed by smart contracts without manual approval for each transaction. Oracle quotes directly change the borrowable amount for each collateralized account. After the attacker used the artificially inflated TONIC as collateral to take away more liquid assets from the pools, the relevant pools would leave a debt gap when the collateral value falls. The final recoverable amount will affect the balance that can be redeemed when each asset pool resumes withdrawals.
After Cronos confirmed that Tectonic had a vulnerability, it suspended the network, and Tectonic asked users to stop interacting with the protocol. Kris Marszalek, CEO of Crypto.com, stated that the Crypto.com app and exchange were not affected, and its security team was assisting with the investigation.
TONIC Surges ~100x in 20 Minutes
Weilin Li categorized this incident as a pump-and-dump lending attack similar to the Mango Markets case. Tectonic accepts its governance token TONIC as collateral with a collateral factor of 20%. The protocol calculates collateral value based on oracle quotes; $100 worth of TONIC can support borrowing up to $20 of other assets.
TONIC has very low trading liquidity. According to Li's tracking, on August 30, the attacker drove up TONIC's price by about 100x in around 20 minutes, then deposited TONIC into Tectonic. After the inflated price entered the protocol's price source, the smart contract simultaneously increased the valuation of this collateral and the account's borrowing limit, allowing the attacker to borrow more liquid assets like USDC and USDT from the depositors' pools.
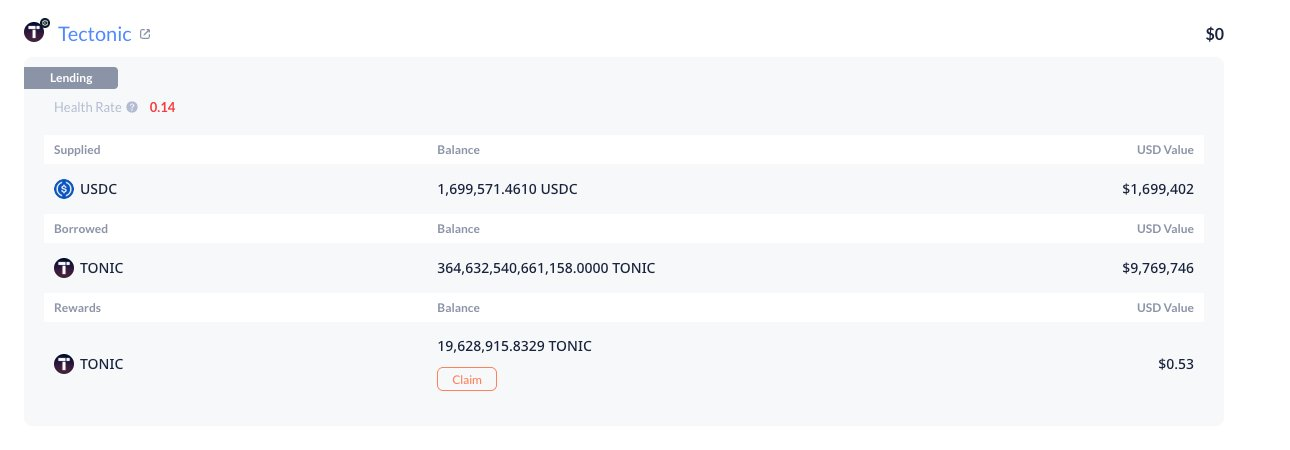
Li identified approximately 364.6 trillion TONIC in the attack position, accounting for about 73% of TONIC's total supply. Based on the manipulated unit price of approximately $0.00000103, the collateral valuation of these tokens within Tectonic was about $375 million.
The assets like USDC and USDT borrowed by the attacker form real debts. After TONIC's price fell, only TONIC collateral that was difficult to sell at the original quote remained in the protocol. Tectonic's liquidators need to first repay part of the attacker's debt and then receive discounted TONIC; when the market cannot absorb such a large amount of TONIC, liquidation transactions cannot recover assets like USDC and USDT at the $375 million collateral valuation, leaving bad debts in the pools.
Li initially identified about $66 million in related funds, of which around $6 million was transferred to Ethereum and about $60 million remained in Cronos addresses; he later found another attacker address holding approximately $8 million, totaling about $74 million across the three parts.
As of August 31, Tectonic's documentation shows that TONIC/USD quotes come from the protocol's internal price source, with data from VVS Finance and Crypto.com Exchange; the oracle updates twice per hour and also updates when the price changes by 1%. Tectonic has not yet released a technical post-mortem, so details such as the specific transactions the attacker used to drive up TONIC's price, how the price source received abnormal quotes, and how the final bad debts will be allocated remain to be officially confirmed.
Same Tactic: Moonwell Left ~$9.13M Debt Three Days Ago
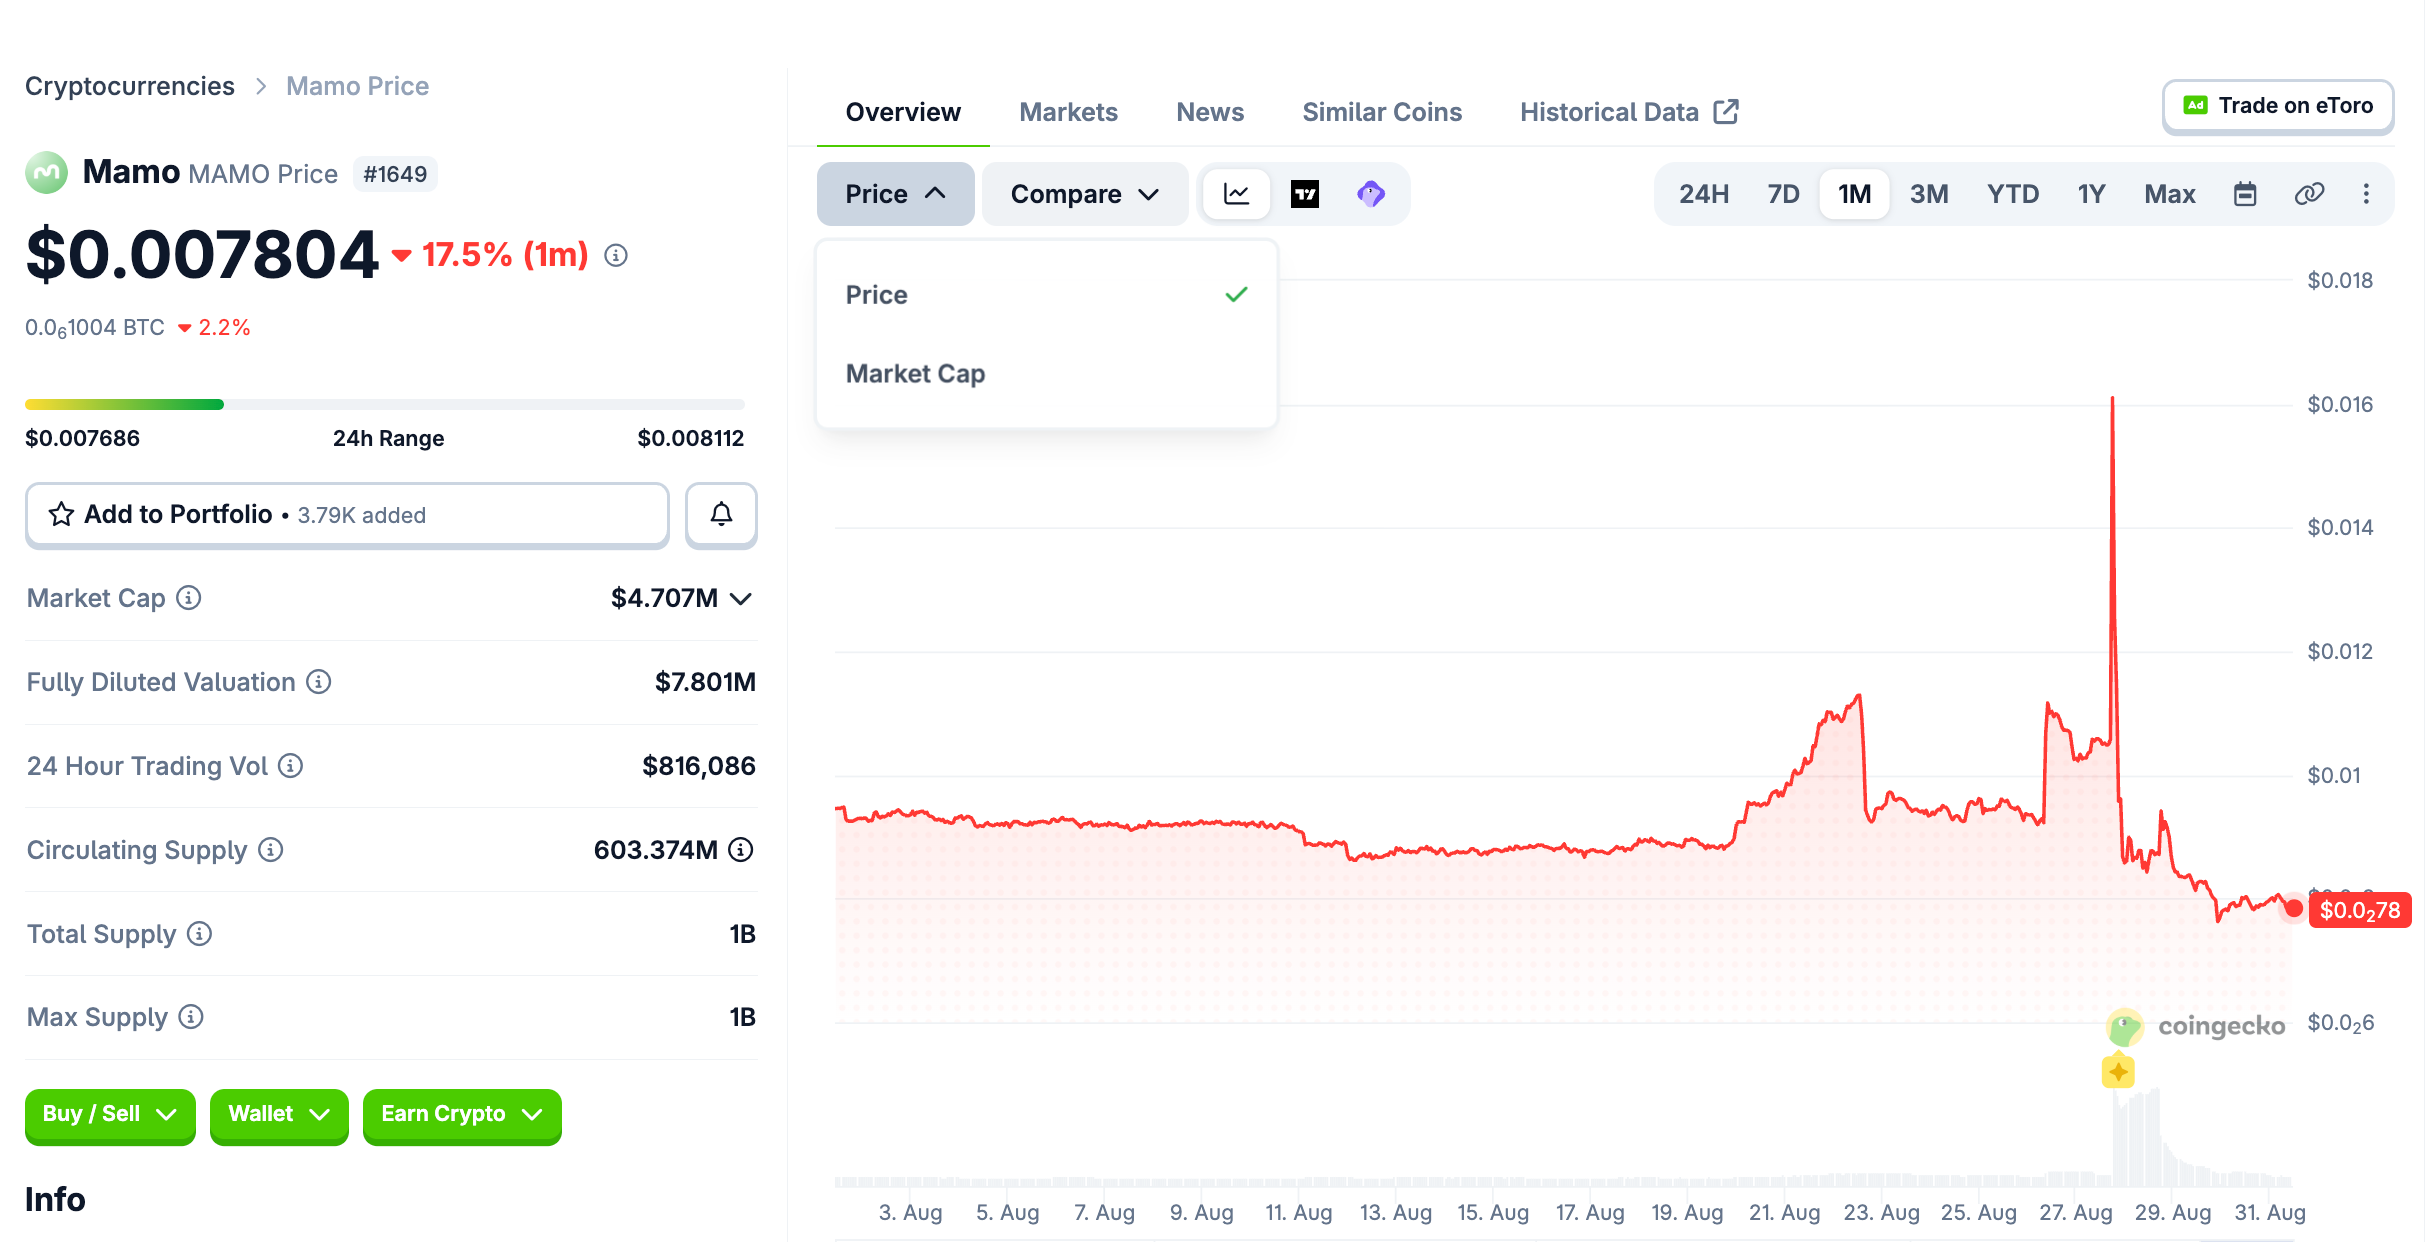
On August 27, the MAMO market of Moonwell, a lending protocol on Base, also suffered from low-liquidity token price manipulation. According to the post-mortem published on Moonwell's governance forum, the attacker invested an initial $1.947 million in USDC, accumulated about 94.31 million MAMO, and directly transferred approximately 53.39 million MAMO to the mMAMO contract. The direct transfer did not mint new mMAMO but increased the underlying assets per mMAMO by about 3.68x.
During the attack on August 27, the MAMO price source rose from approximately $0.0106 to $0.4313. After both the collateral share and oracle quote increased, the attacker completed 18 borrowings, withdrawing cbBTC, WETH, USDC, and wstETH with a total value of about $11.03 million. Liquidation started 32 seconds after the last borrowing, and Moonwell finally recorded approximately $9.131 million in remaining debt.
The 2022 Mango Markets incident was similar. The U.S. Commodity Futures Trading Commission (CFTC) disclosed that in October 2022, the attacker drove up MNGO's price by more than 13x in about 30 minutes, then withdrew over $110 million in assets using the inflated position value. The attacker later returned about $67 million to Mango Markets and kept around $47 million. The CFTC filed an enforcement action in 2023, classifying it as the agency's first case involving oracle manipulation on a decentralized exchange.
Tectonic and Moonwell were damaged consecutively within four days. Both incidents involved a sharp rise in the price of low-liquidity tokens, followed by smart contracts expanding borrowing limits based on the inflated quotes. Similar projects may all need to pay attention to this.
Over $60M Remains in Cronos Addresses
To date, Cronos' chain halt has restricted the attacker from further cross-chain fund transfers and suspended withdrawal, repayment, collateral addition, and liquidation operations on the network. Tectonic users cannot adjust their lending positions, and other applications on Cronos cannot submit or confirm transactions.
Whether the assets remaining in the attack addresses can be frozen or returned depends on the handling plan adopted when Cronos resumes block production and Tectonic's final accounting of related debts and pool balances. If bad debts occur in the protocol's pools, Tectonic also needs to announce the gap in each asset pool, the withdrawable balance, and user compensation arrangements.
As of August 31, Tectonic has not confirmed the exact loss amount and attack cause, and Cronos has not announced the block production resumption time or the disposal plan for the attack assets.