Right now, what we should focus on isn't the narrative—it's who can mint coins, who can change parameters, and whether anyone is actually looking at proposals when they're posted on-chain.
Written by: Ma He, Foresight News
In less than a week, three crypto protocols have become targets of attackers.
On August 20, payment public chain Keeta Network set its mainnet to read-only, citing a security issue in a single component, and subsequently issued a 72-hour demand for the attacker to return funds; on August 22, metaverse project The Sandbox suffered a cross-chain minting attack, where attackers printed a large amount of SAND on Base and BNB Chain. The project team cut off the bridges between the two chains, and security agencies estimate the actual reserve funds siphoned off amount to approximately $670,000; on August 23, fixed-rate lending protocol Term Finance had approximately 2,843 ETH and 1.68 million USDC transferred out of its treasury due to the execution of a governance proposal, resulting in losses of around $8.5 million.
These three incidents are unrelated and have different attack vectors, but all occurred within the same week.
Keeta: Mainnet Set to Read-Only Status
Keeta is a payment-focused public chain. In an update on August 20, its co-founder and CEO Ty (X account @schenkty) suddenly posted a tweet stating that the root cause of the security incident had been identified, the issue was limited to the affected component, and did not involve the anchoring system or external connection systems; KTA deployed on Base was not affected.
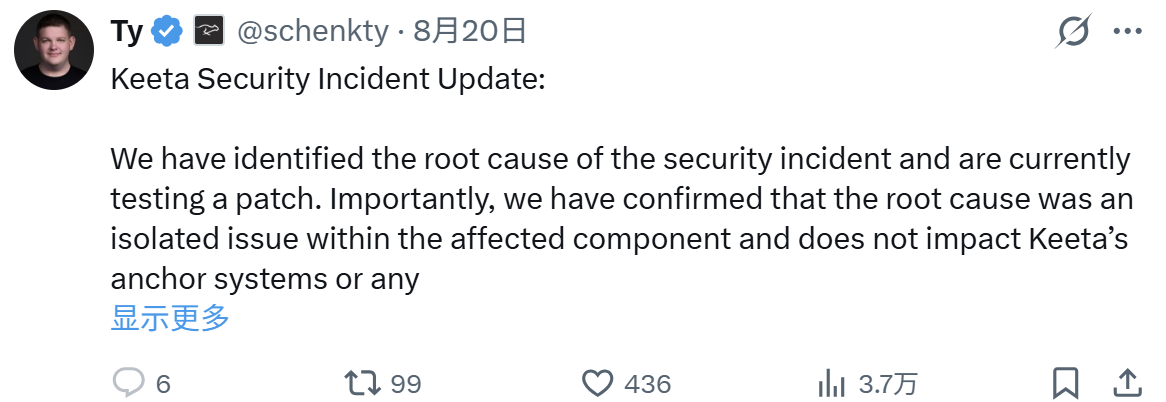
As a precautionary measure, the mainnet was placed in read-only mode, and full operation will resume after the patch is tested and additional safeguards are added. The team also stated that it is evaluating how to fully compensate affected users, and that strategic reserves can cover the damaged funds if needed.
The official has not yet released the audited "total stolen amount". Lookonchain monitored that a new address received approximately 9.3 million KTA (worth about $685,000 at the time) and around 2 billion GALA via a cross-chain bridge, then sold them for approximately 1,902 ETH (about $3.64 million).
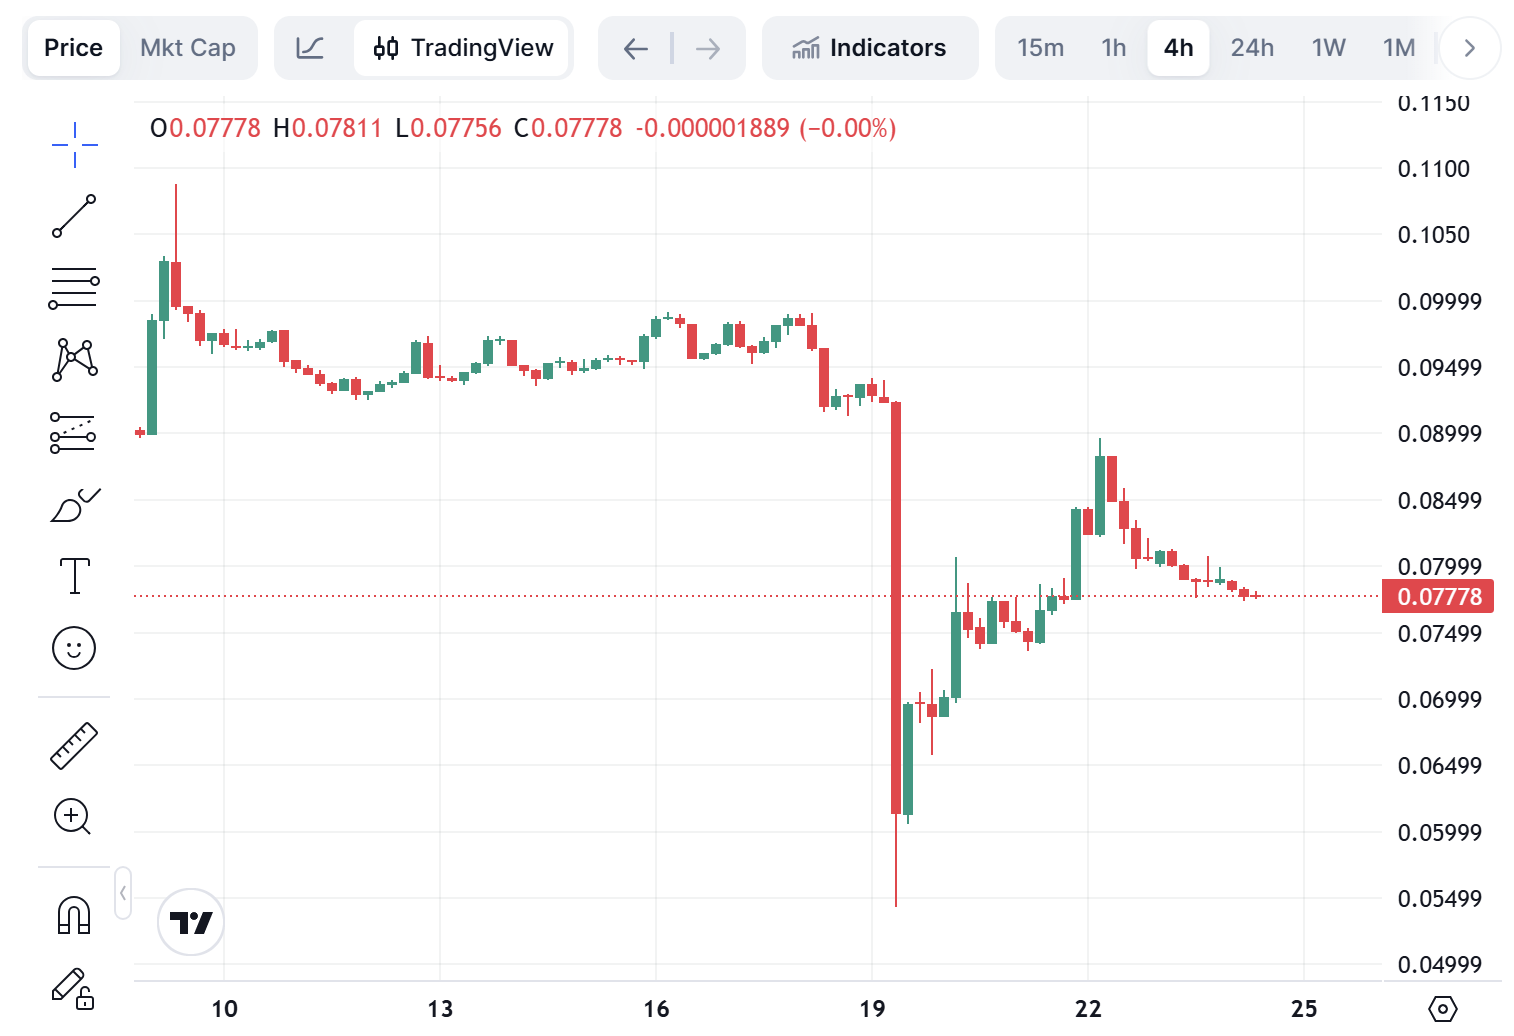
On August 19, the price of KTA plummeted from a high of $0.09 to a low of $0.05, a drop of about 37%, and has now rebounded to $0.077.
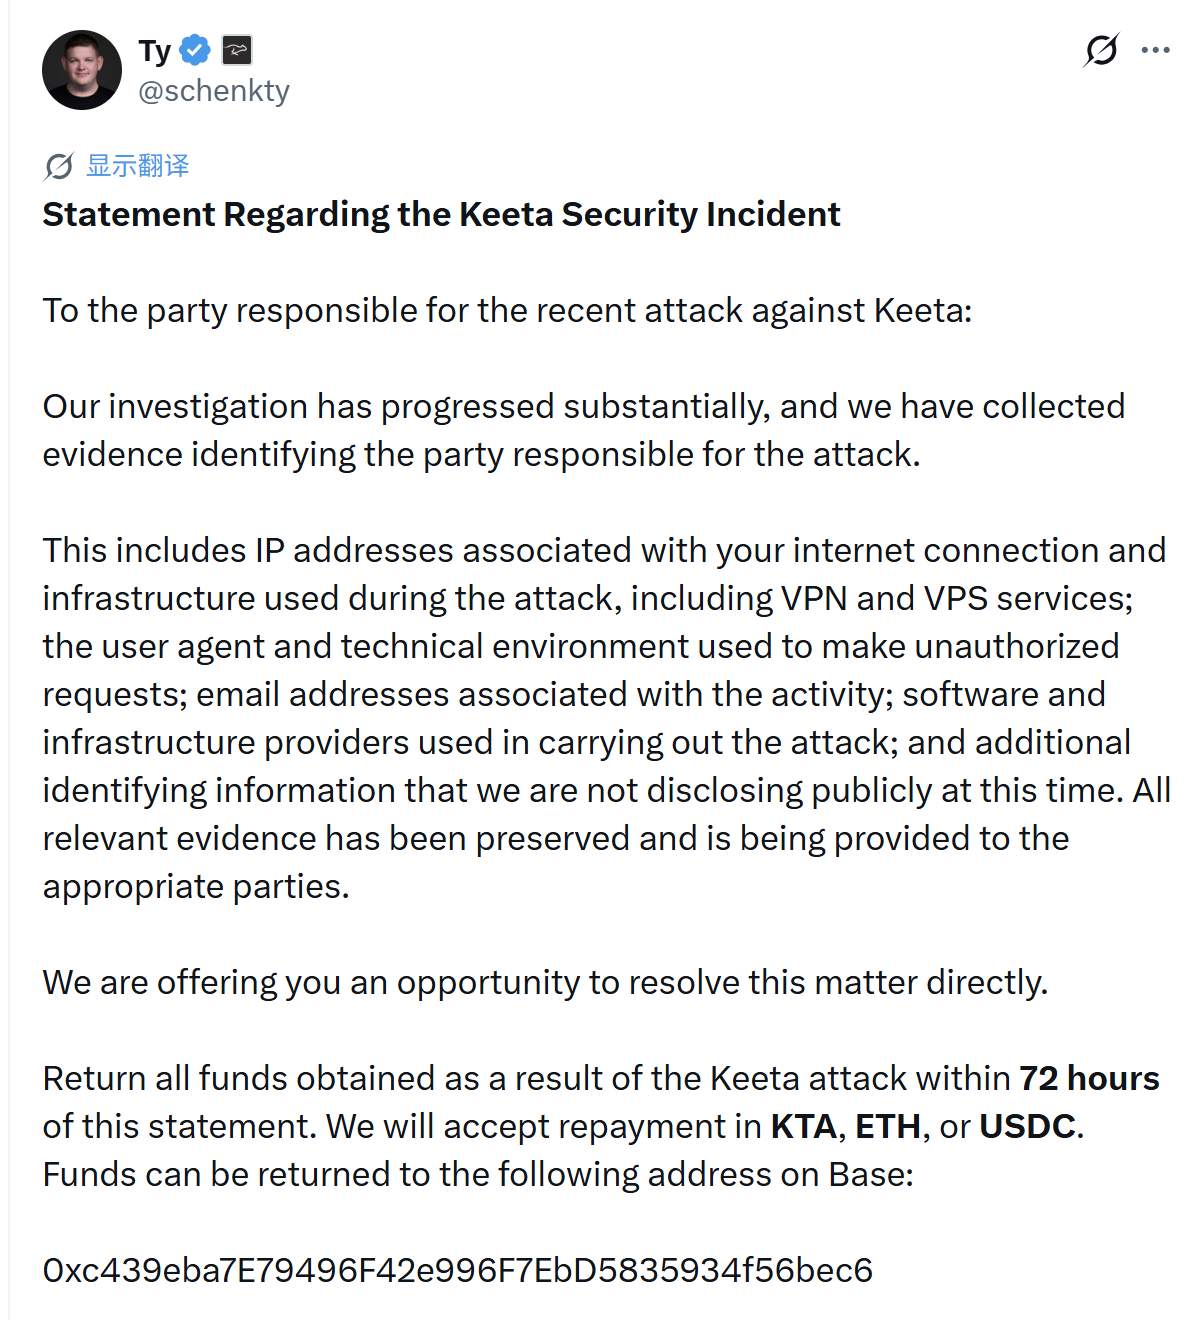
On August 22, Ty issued another statement saying that the investigation had made substantial progress and that evidence pointing to the attacker had been collected, including attack-related IPs, VPNs and VPS used, user agents and technical environments during unauthorized requests, associated emails, and information about software and infrastructure service providers; the evidence has been preserved and submitted to relevant parties. The statement demands that the attacker return all proceeds within 72 hours, which can be sent to a Base address in KTA, ETH, or USDC. If fully returned, Keeta is willing to discuss a bug bounty and settle without pursuing legal liability; if overdue, it reserves the right to legal accountability and fund recovery.
The official promised to release a complete technical report after the investigation and verification. As of August 24, the mainnet remains read-only, no compensation details have been released, and whether the 72-hour window will be honored is still unknown.
The lesson from this incident is not complicated: when an application chain sets "who can change permissions" to be lenient by default or can be bypassed through combinations, shutting down the chain is often faster than applying a patch. Keeta's choice to disclose some off-chain clues and set a return deadline is rare in recent theft cases, but whether the funds are returned and whether the report matches the on-chain data are the standards to test this approach.
The Sandbox: Counterfeit Coins Minted in Astronomical Numbers
On August 22, the SAND cross-chain contract of The Sandbox deployed on Base was attacked. The attacker took over LayerZero's representative permissions via approveAndCall, continuously minting SAND without collateral on the Ethereum mainnet, and the attack spread to BNB Chain. The core layer of the LayerZero protocol was not compromised.
The project team immediately cut off the two-way bridges with Base and BNB Chain. The nominal增发 was reported to be about 14.9 billion coins, with a nominal spot exposure of hundreds of millions of dollars, but the actual funds siphoned from the Ethereum reserve and cashed out were approximately 14.75 million SAND and about 80 ETH, equivalent to around $670,000. The project team stated that SAND on Ethereum and Polygon, user wallets, and mainnet collateral were not affected.
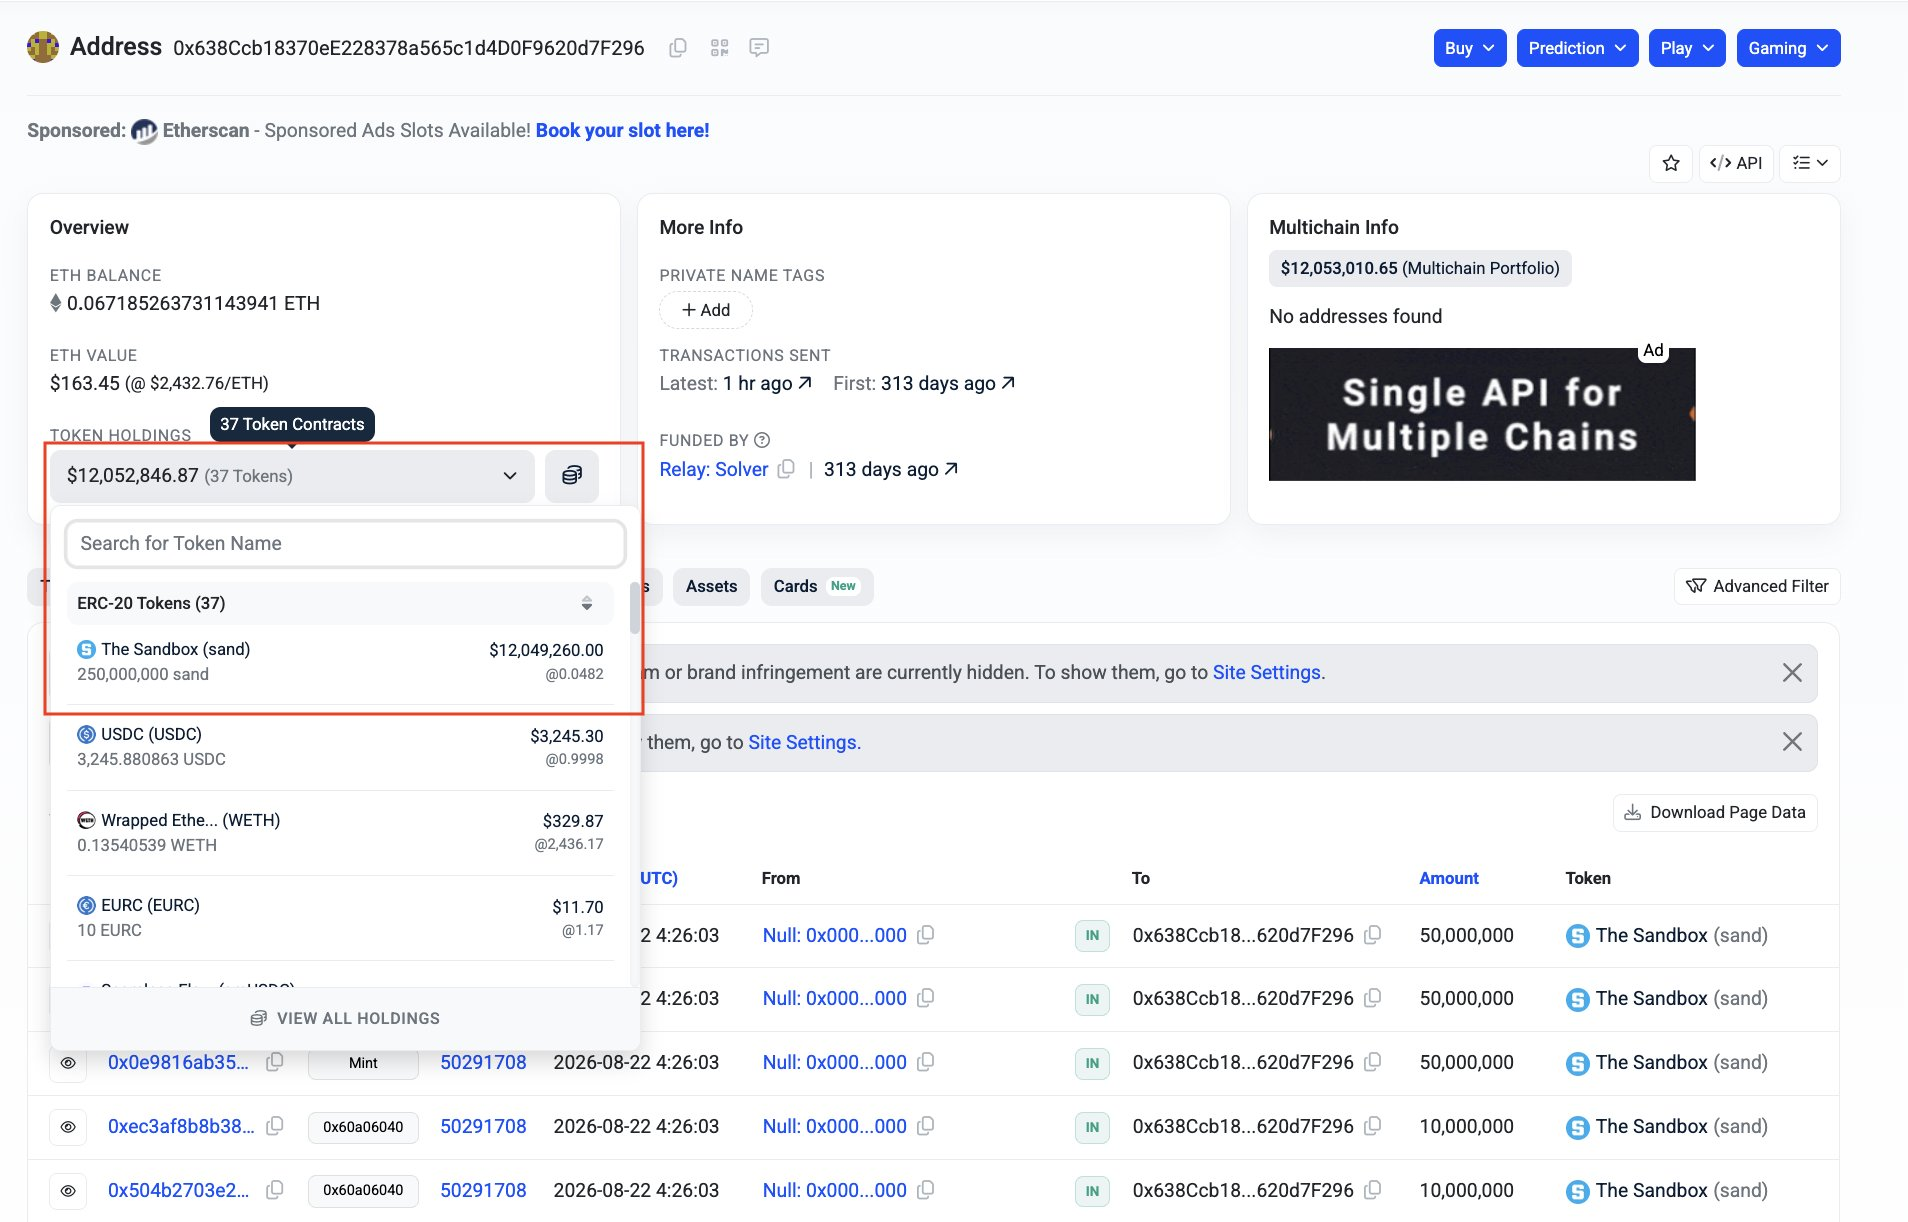
SAND cross-chain uses LayerZero's OFT: minting on the opposite end should correspond to locking on the mainnet, and node representatives decide who can mint on the target chain. The vulnerability was in the project team's contract's approveAndCall, which was used to change delegation permissions, allowing fake cross-chain minting to take effect.
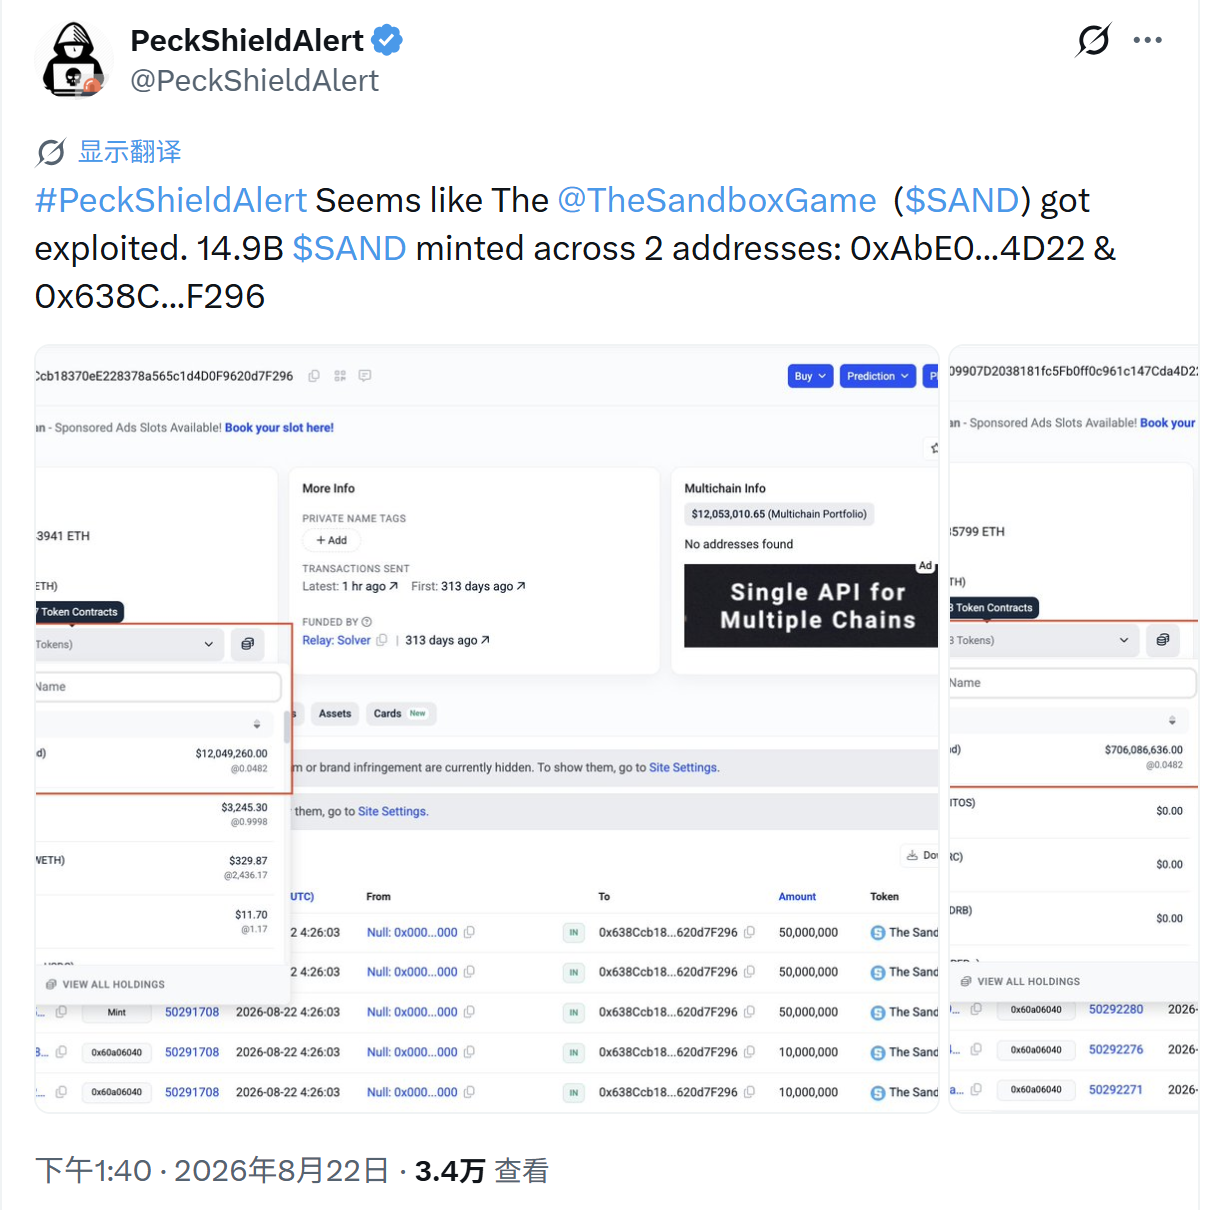
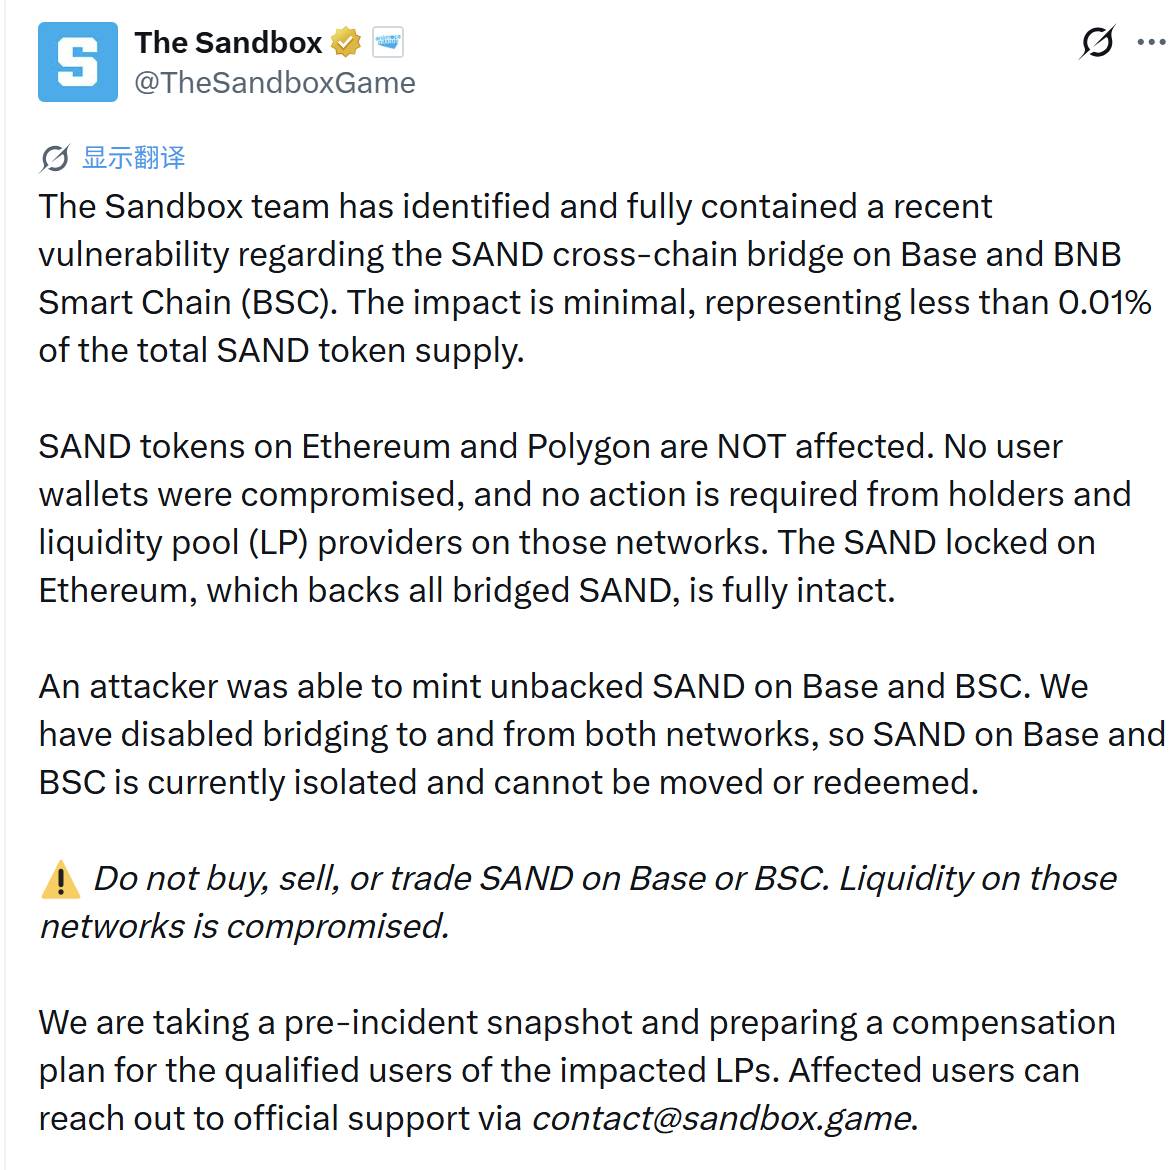
The official stated that the vulnerability has been contained, affecting less than 0.01% of the total supply, and reminded investors not to trade SAND on Base or BSC. Exchanges Upbit and Bithumb have suspended deposits and withdrawals.
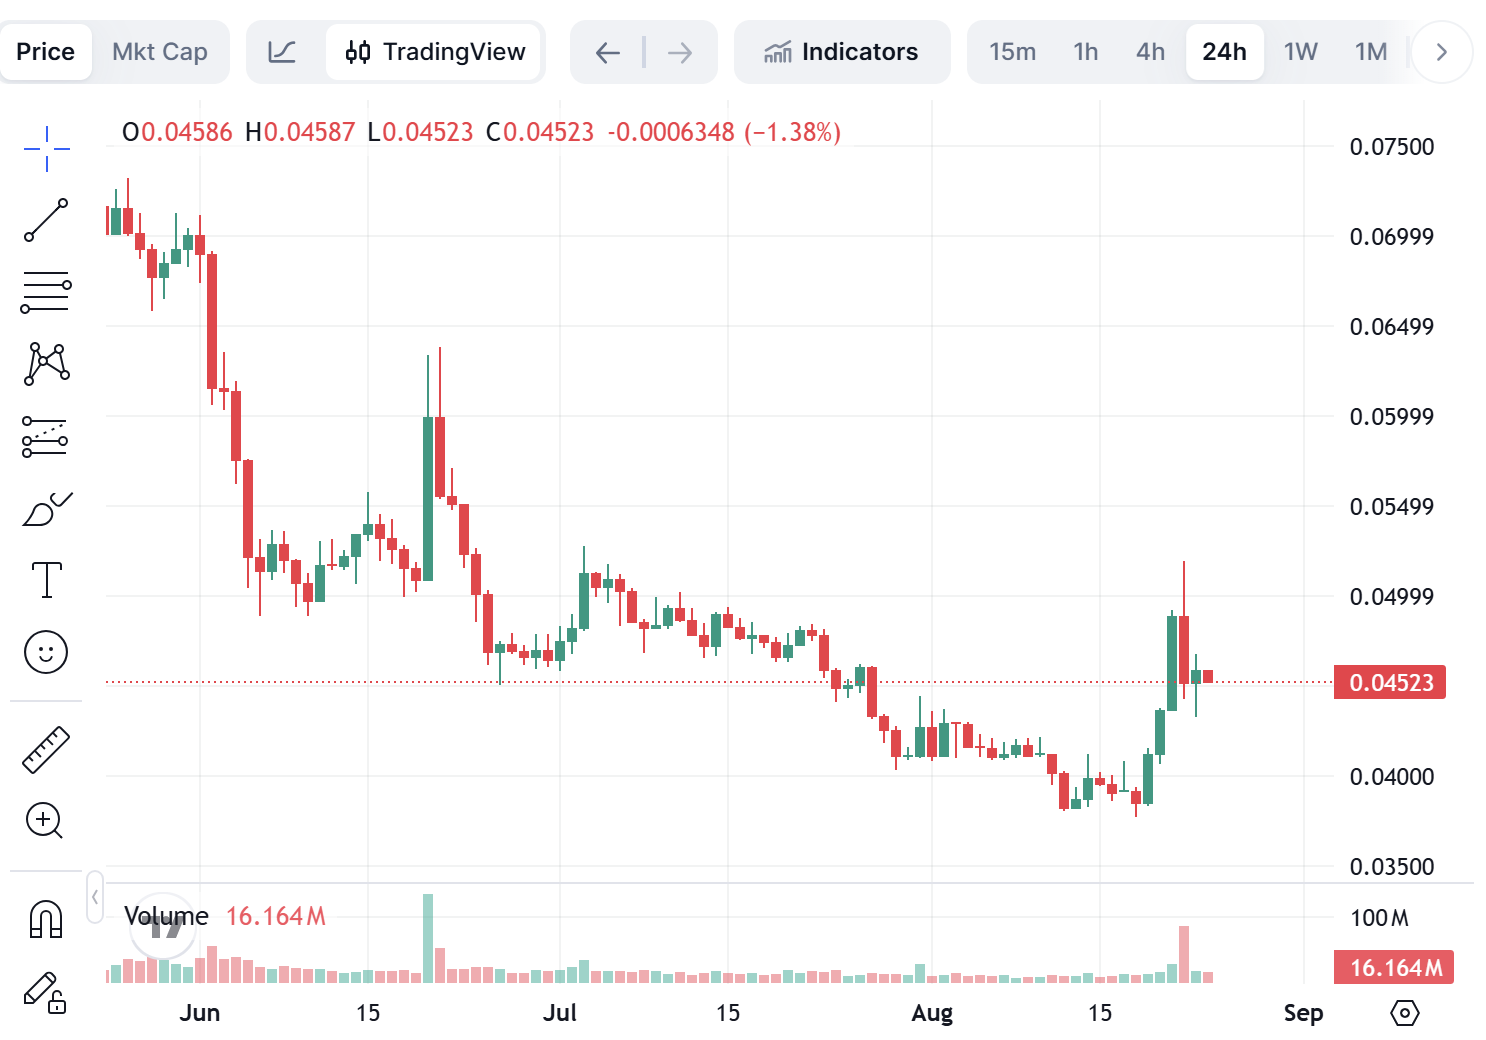
As of press time, the price of SAND has dropped from $0.05 to $0.045.
Term Finance: Proposal Hung On-Chain for Six Days Without Veto, Treasury Transferred via Governance Process
Term Finance is a fixed-rate lending protocol on Ethereum. On August 23, an Ethereum transaction executed a governance proposal that had been publicly posted on-chain for about six days. There were zero veto votes on the voting page. The proposal included closing the original approximately 7-day transaction timelock, then transferring about 2,842 WETH from the ETH Meta Vault.

About 20 minutes later, a second transaction transferred approximately 1.68 million USDC from five USDC vaults and converted them to DAI. PeckShield estimates the attacker took about 2,843 ETH (worth about $6.9 million at the time) and 1.68 million USDC.

This incident was not a smart contract reentrancy or oracle manipulation; instead, the governance process followed the protocol design: "submit—wait—no veto—execute". External analysis suggests that the attacker, given the low circulation of governance tokens, obtained nearly all voting rights for some USDC strategy vaults and about 90% control over the ETH Meta Vault, then framed the fund transfer as a valid governance action.
As of now, Term Labs stated that all Term Meta Vaults have been closed, DAO governance roles have been revoked, this closure is irreversible, and further deposits are permanently prohibited. Withdrawals are still allowed. The official said that based on current investigations, the underlying Term protocol and its direct lending market were not affected, and it is coordinating with external security teams for remediation and recovery work.

Governance attacks are not uncommon in recent years. They are particularly effective when voting rights are concentrated and participation is low.
In July this year, BonkDAO's treasury was attacked via a malicious governance proposal, with BONK tokens worth about $20 million stolen. The attacker's related address purchased BONK via a CEX wallet before the proposal was initiated, then manipulated the vote, and finally transferred the large sum of funds "publicly" via the governance process.
Keeta shut down the entire mainnet, first closing component permissions before moving to compensation and 72-hour recovery efforts. Sandbox cut off the bridge—on paper, the minted amount was absurd, but only about $600,000 in reserves were actually cashed out, and the dispute will focus on how to compensate LP snapshots. Term's proposal sat for six days with zero veto votes, the timelock could be closed by the same proposal, and about $8.5 million was transferred via the governance process.
Right now, what we should focus on isn't the narrative—it's who can mint coins, who can change parameters, and whether anyone is actually looking at proposals when they're posted on-chain.